

Roles and access
Your organization has four roles: administrator, developer, manager and member. The role decides which sections of the cabinet a person sees and what they may change inside them.In the role selector on the Organization page the four are labelled Admin, Developer, Manager and Member, and the controls that refer to the last one use the same word — Visible to members on an agent, for example.
Sections by role
● available · ◐ available with a restriction · — not shownRunning the business
¹ View only: adding cards and changing the layout and tabs is for administrators and developers.
² A manager and a member run the whole campaign lifecycle — see below.
³ Without the full call log export; reports — their own only.
⁴ The Registry tab, yes; the Capture settings, no.
⁵ Only on the US market profile, and read-only: the rules themselves are set by the platform.
Building agents
¹ Only an administrator can connect WhatsApp and SMS numbers and bind an agent to them.
Demo links are not a separate section but the Share demo link… dialog in an agent’s menu; it is available to administrators and developers.
Administration
¹ Closed even for reading.
² Manages users; the organization settings are read-only — see the manager role.
³ Without the Defaults for new agents section.
⁴ View only: the alerts and the delivery log are visible; alerts cannot be created, changed or deleted.
The member role in detail
An open section does not mean full rights. A member’s list of permitted changes is closed by default and enumerated by name: anything not on it is forbidden to a member in every section they see. Can change- A campaign, end to end — create, edit, upload contacts, launch, pause, resume, cancel, decide on matches against the do-not-call registry, and add a batch of calls
- Dialing presets — create, edit, delete
- The do-not-call registry — add, remove, import, review
- Reports — build and download their own
- Report templates — save, edit, delete
- Their own interface settings
- Review incidents — mark them reviewed, resolved, a false positive, or reopen them
- Re-run call analytics or retry a webhook from the call card
- Open an agent’s settings from History or the call card
- Export a call log — that is personal data: transcript, numbers, variables. A member has no Download log button in the call card at all
- See system events in the call card — the call card opens in the simple view only: the conversation without system events and without the observer card
- Delete a report, including their own; other people’s reports they do not see at all
- Open API keys — the section is closed even for reading
- Configure do-not-call capture — that is agent behaviour, not registry content
- Set defaults for new agents
- Manage users and the organization
- Edit voicemail phrases and call screener phrases
Which agents a member sees
The Agents section and the builder are closed to a member, so the only place they meet agent names is the choice of an agent for a campaign — and that list is filtered. An agent marked hidden from members is not offered to them for a new campaign, and the platform refuses such a choice on the server rather than merely leaving it out of the list. Administrators and developers see every agent and are the only ones who can change the setting. A member does not see the calls of a hidden agent anywhere: they are absent from History and its totals, from reports and from the dashboard’s recent calls, and the card of such a call does not open. The incidents of those calls are not shown either. Once the agent is made visible again, its calls and incidents come back. A campaign already running on an agent that was hidden later stays manageable: it can be paused and resumed. A draft campaign on such an agent cannot be launched by a member — the pre-launch check stops it with The campaign agent is hidden from members; pick a visible agent instead. A member does not see technical findings about the agent’s settings when launching or resuming a campaign or adding contacts: warnings about the recognition, synthesis and model providers are not shown, and the errors that block the launch are folded into one line, The agent is not configured correctly — contact support. The details are seen by an administrator and a developer. See Launching a campaign.The manager role
A manager has everything a member has — the same sections, the same campaign rights, the same limits, including which agents they see — and three more things: they manage the users of their own organization, and edit its voicemail phrases and call screener phrases. A person who has left loses access as soon as the manager deactivates them. In their own organization a manager can:- add a user with the role Member or Manager;
- change a role between Member and Manager — including giving or taking away the manager role;
- deactivate and activate an account;
- reset a password — a new temporary password is issued;
- reset 2FA — when a user has lost the phone with their authenticator app.
- Administrators and developers are listed but cannot be changed: in the ⋯ menu of their row, Change role is inactive with the hint “Only an administrator can change this role”, and there are no other actions.
- The organization settings are visible to a manager on the Settings tab, but cannot be changed.
Organization users
Users are on the Users tab of the Organization page; it is open to administrators and managers. The user list has search, a Role filter and pagination: in an organization of a hundred people you find someone by typing a name rather than by scrolling. Next to the name in a user’s row there are marks: you — your own account, Invited — the user has never signed in, Deactivated — the account is switched off.Temporary password
A temporary password is issued when a user is added and when a password is reset. It is shown once — copy it and pass it to the user. At the first sign-in with the temporary password the user is asked to set their own.Resetting 2FA
If a user has lost the device with their sign-in codes, their 2FA is reset by whoever can reset their password: ⋯ in the user’s row → Reset 2FA. After confirmation all their 2FA devices are removed and all their sessions are ended; the password stays the same. At the next sign-in the user sets up 2FA again. If the user had no 2FA, nothing changes. You cannot reset your own 2FA this way — manage it in your own account.Your account: password, 2FA and session
Every user has the Account section on the Settings page: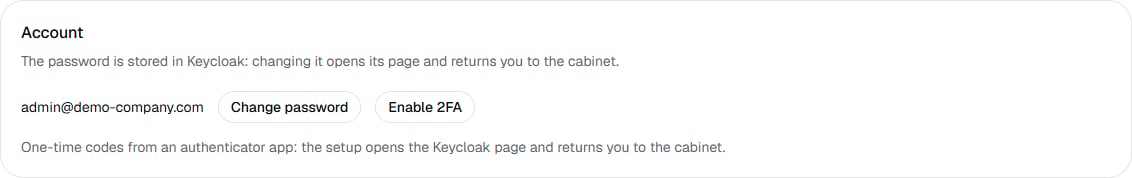
- Change password opens the sign-in page and returns you to the cabinet after the change.
- 2FA — one-time codes from an authenticator app. While 2FA is off, you see the Enable 2FA button. When it is on, you see 2FA is on and the list of devices with the date each was added: Remove on each and Add device. Removing and adding open the sign-in page; if you signed in more than 5 minutes ago, it asks you to sign in again.
Every change is confirmed and logged
Changing a role — ⋯ in the user’s row → Change role. A side panel opens with the user’s name and email, the name of their organization, and the cards of the roles you may give. Once a different role is selected, the lists Gains access and Loses access appear under the cards — what the user gets and loses; an empty list is not shown. Save becomes active once a different role is selected; Cancel closes the panel without changes. Deactivating, activating, resetting a password and resetting 2FA ask for confirmation in a dialog. The Deactivate button in the dialog is marked as a destructive action. Adding a user, changing a role, deactivating and activating are written to the audit log, whoever does it — an administrator or a manager. So are a password reset and a 2FA reset. Nobody can change their own role, administrators included: in your own row Change role is inactive with the hint “You cannot change your own role”. Someone else has to do it. For a deactivated account the item is inactive too — activate the account first. You cannot deactivate yourself either: your own row has no Deactivate user item.There is no user deletion — there is deactivation
An account is not deleted but deactivated: the person loses access while the record stays visible in the list and can be switched back on. It works this way because an email address is globally unique: a taken address could otherwise be neither freed nor recovered. A deactivated account comes back only through Activate. Adding a new user with the same address is refused: “A user with the email … already exists in the organization. If the account is deactivated, activate it in the list”. The returning person gets their old account back, with its history, rather than a new one. To change the role of a deactivated account, activate it first. If the address is already taken outside your organization, adding the user is refused with “Could not create the user: the specified email is unavailable”.Where developers stop
A developer can do everything an administrator can, except the following, which stays with the administrator:- users and the organization settings;
- locking components and editing locked components;
- connecting WhatsApp and SMS numbers in the Channels section and binding an agent to them.